- engineering
- umkm
- startup
PP 33/2026: Website Compliance Checklist for Indonesia
PP 33/2026 takes effect January 16, 2027. A website compliance checklist for Indonesian businesses: privacy notice, consent, data rights, DPIA, and technical controls.
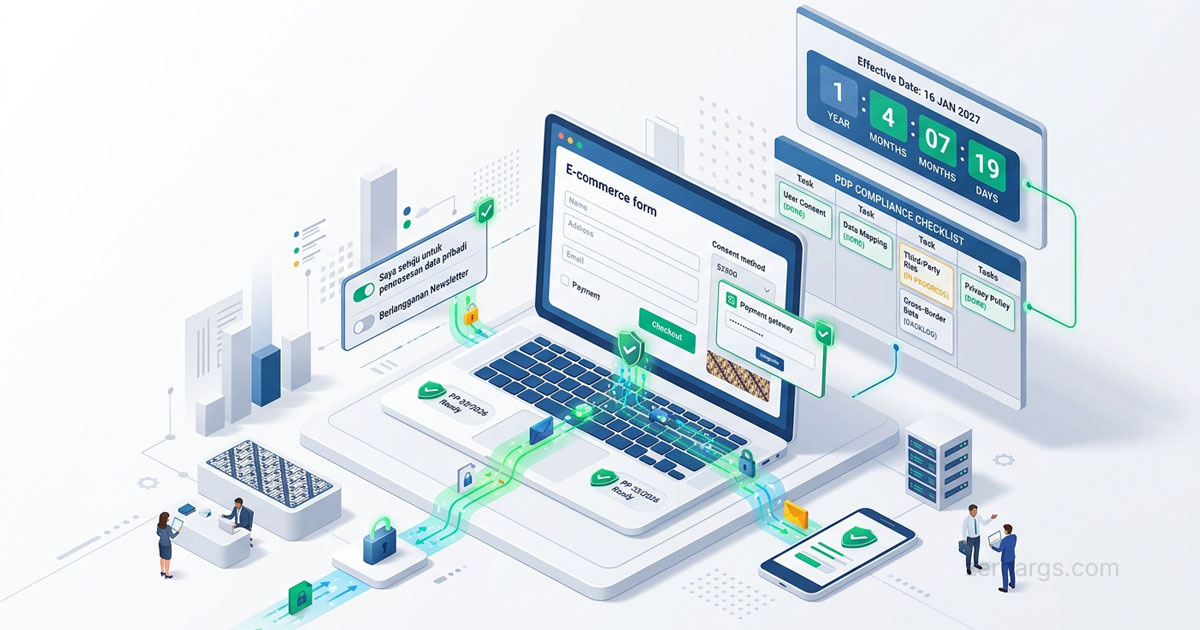
PP 33/2026 finally delivers the operational detail Indonesian digital businesses have been waiting for since the Personal Data Protection Law took full effect. This Government Regulation — the implementing rule for Indonesia's PDP Law (Law 27/2022) — was promulgated on July 16, 2026 and becomes effective on January 16, 2027. That gives you roughly four months to align your website, checkout forms, payment gateway integrations, and internal procedures before administrative sanctions can apply. If you operate your own online store for an MSME in Indonesia, this is no longer abstract legal theory — it is an engineering backlog item with a fixed deadline.
1. What PP 33/2026 Is and Why Your Business Website Matters Now
PP 33/2026 (Government Regulation No. 33 of 2026 on the Implementation of the Personal Data Protection Law) spans 12 chapters and 225 articles, turning PDP principles into enforceable operational requirements. Before this regulation, many businesses complied with the PDP Law in principle since the transition period ended in October 2024 — but without uniform guidance on privacy notice format, consent evidence, or when a DPIA (Data Protection Impact Assessment) is mandatory.
For business websites, PP 33/2026 matters because nearly every online store collects personal data: names, shipping addresses, phone numbers, order history, and often payment metadata through gateways such as Midtrans, Xendit, or Doku. Every registration form, analytics cookie, chat widget, and CRM webhook is a processing point that now has explicit documentation standards.
Four months until January 16, 2027 is enough for baseline compliance — but not if you wait until late December. Privacy notice updates, consent banners, and data-subject request workflows need staging tests, business-owner approval, and third-party vendor alignment. That rarely finishes in a single week.
2. New Obligations That Directly Affect Your Website and Forms
PP 33/2026 clarifies several duties that were only implied under the PDP Law. Here is what most directly affects the team running your website:
Lawful basis before collection. You cannot store customer data in a database without identifying the legal basis — consent, contract performance (for example shipping an order), or legal obligation. Technically, this means checkout forms must not pre-check marketing checkboxes, and optional fields must genuinely be optional.
Accessible, accurate privacy notice. PP 33/2026 requires minimum information: controller identity, data categories collected, processing purposes, legal basis, retention periods, recipients (including vendors), data-subject rights, and a contact point. The notice must be available before collection — not buried in a tiny footer link.
Verifiable consent evidence. For consent-based processing (newsletters, analytics cookies, marketing profiles), you must retain proof: who consented, when, which policy version applied, and what they agreed to. Manual spreadsheets do not scale; at minimum, store records in your database with timestamps.
Notice for indirectly sourced data. If you obtain customer data from a third party (for example marketplace imports or lead generation), data subjects must be informed within 30 business days. Websites that sync orders from Tokopedia or Shopee into an internal CRM need a notification workflow for this scenario.
3. Required Pages Checklist: Privacy Notice, Consent, and Data Rights
Three pages or components should exist on every business website that collects personal data:
Privacy Policy page — not a copy-paste foreign template. Content must reflect your actual systems: a table of data types, purposes, retention, and vendors. Rows teams often forget:
| Data type | Purpose | Retention | Vendor/recipient |
|---|---|---|---|
| Name, address, phone | Order fulfillment | 5 years after last transaction | JNE, J&T (shipping data) |
| Order confirmation, newsletter (if consented) | Until unsubscribe + 30 days | Resend, Mailchimp | |
| Payment metadata | Transaction reconciliation | Per tax requirements | Midtrans/Xendit |
Separate consent forms — do not bundle marketing consent with core checkout terms. A "I agree to receive promotions" checkbox must default to unchecked, with a link to the relevant policy. Store consent_type, policy_version, timestamp, and user_id or email.
Data-subject rights channel — provide a dedicated email or form for access, correction, deletion, or portability requests. PP 33/2026 requires responses within a reasonable timeframe. On the technical side, prepare an internal query or script to export user data from users, orders, and addresses tables without manual production access every time.
If you already built foundations from our practical PDP guide for business web apps, PP 33/2026 is the detail layer on top — not a replacement.
4. Technical Implementation: Consent Storage, Cookie Banner, and Data Deletion
Engineering teams must translate legal duties into system behavior. Four priority implementations:
Cookie and tracking consent. If your site loads Google Analytics, Meta Pixel, or Hotjar, activate tags only after users consent to non-essential cookie categories. Use Consent Mode v2 or a lightweight CMP. Log the user's decision — do not merely hide the banner.
Consent records in the database. A minimal schema example:
CREATE TABLE consent_records (
  id UUID PRIMARY KEY,
  user_id UUID REFERENCES users(id),
  consent_type VARCHAR(50) NOT NULL,  -- 'marketing', 'analytics', 'terms'
  policy_version VARCHAR(20) NOT NULL,
  granted BOOLEAN NOT NULL,
  ip_address INET,
  created_at TIMESTAMPTZ DEFAULT NOW()
);
Data deletion endpoint. Provide an internal route or admin tool that deletes or anonymizes user data across all related tables — including session cache and logs that store PII. Document data that cannot be deleted due to tax obligations (transaction evidence) and how you anonymize it instead.
Encryption and access control. HTTPS is mandatory (standard in 2026), but also verify: are database backups encrypted? Can CS staff only view customers they serve? PP 33/2026 reinforces proportionate security obligations — for MSMEs, a password manager and 2FA on the admin panel are baseline expectations.
5. Vendors and Cross-Border Transfers: Audit Payment Gateways and Cloud
Almost no business website stands alone. PP 33/2026 governs the relationship between controllers (you) and processors (vendors processing data on your behalf). Vendor audit checklist:
- Is there a data processing agreement (DPA) or privacy clause in the vendor's Terms of Service?
- In which region is data stored? GCP asia-southeast2 (Jakarta) or AWS ap-southeast-3 reduces cross-border transfer risk compared to default US regions.
- Does the vendor support data deletion on request?
- Are sub-processors (for example infrastructure behind your payment gateway) documented?
Transfers outside Indonesia require mechanisms defined in PP 33/2026 — adequacy decisions, standard contractual clauses, or explicit data-subject consent. If overseas support staff can access your CRM dashboard, that is also a transfer that needs mapping.
Connect this audit with PSE registration with Komdigi if your website requires it — both are often completed in parallel.
6. Lightweight DPIA for High-Risk Features
A Data Protection Impact Assessment (DPIA) is mandatory for high-risk processing. On business websites, features that commonly trigger a DPIA include:
- AI chatbots that store customer conversation history (including WhatsApp Business API integrations)
- Automated profiling — product recommendations based on browsing behavior that lead to significant decisions
- Sensitive data processing — health, religion, or detailed financial data beyond standard transactions
- Large-scale systematic monitoring — heatmaps plus session recording across the entire site
A DPIA does not need to be a 50-page document. For MSMEs, one to three pages answering what data is processed, what risks exist, what controls are applied, and what residual risk is accepted is a solid starting point. If you are planning an AI WhatsApp customer service chatbot, include DPIA in the planning sprint — not as a post-launch footnote.
7. Incident Preparedness: 3×24 Hour Notification and Technical Runbook
PP 33/2026 reinforces the duty to report personal data protection failures (data breaches) to authorities within 3×24 hours of identification, and to data subjects when risk is significant. A minimal technical runbook:
- Detection — alerts for anomalous admin logins, unusual database access, or customer reports.
- Containment — rotate API keys, revoke sessions, block IPs if needed.
- Inventory — what data was exposed, how many subjects, since when.
- Notification — templates for authority and affected customer emails.
- Documentation — incident timeline for audit.
Store the runbook somewhere accessible when servers are down — not only in an internal wiki that might be part of the breach.
8. Comparison Table: Baseline Compliance vs PP 33/2026 (January 2027)
Use this table for a quick gap assessment before January 16, 2027:
| Area | Before PP 33/2026 (common practice) | After PP 33/2026 (operational requirement) |
|---|---|---|
| Privacy notice | Generic template in footer | Specific content, accessible before collection |
| Consent | Pre-checked checkbox | Explicit opt-in + stored evidence |
| Data-subject rights | Informal email to admin | Documented procedure + response SLA |
| Vendors | Not audited | DPA, sub-processor mapping, data region |
| Cross-border transfer | Not mapped | Legal mechanism (adequacy/SCC/consent) |
| Data incidents | No runbook | 3×24 hour report + subject notification |
| DPIA | Not performed | Mandatory for high-risk processing |
| DPO (PPDP) | Owner as informal PIC | Formal appointment when criteria met |
If more than half the right column is still empty, prioritize privacy notice and consent storage this week — the two items with the highest impact and most measurable effort.
Conclusion
PP 33/2026 turns personal data compliance from static documents into auditable system behavior. Your business website — checkout forms, analytics cookies, payment gateway integrations, and database backups — is the first place regulators and customers will look if a complaint or incident occurs. Four months until January 16, 2027 is enough to finish the foundation if you start now: an accurate privacy notice, recorded consent, data-subject request procedures, vendor audit, and an incident runbook.
At Zero Args Technology, we help MSMEs and product teams in Indonesia build websites and apps with data compliance designed from day one — not patched before a regulatory deadline. Start a conversation if you want to assess PP 33/2026 gaps on an existing website or plan privacy foundations for a new product.
Frequently asked questions
When does PP 33/2026 take effect?
PP 33/2026 was promulgated on July 16, 2026 and takes effect on January 16, 2027 — six months after enactment. Businesses that process personal data through a website or app should complete adjustments before that date.
Do small businesses with a simple website need to comply with PP 33/2026?
Yes. PP 33/2026 applies to anyone who collects or processes personal data, including MSME online stores. Documentation depth and security controls scale with risk, but baseline obligations such as a privacy notice and lawful processing basis still apply.
How is PP 33/2026 different from the PDP Law already in force?
Indonesia's PDP Law (Law 27/2022) established principles and data-subject rights since October 2024. PP 33/2026 adds operational rules: privacy notice format, consent mechanisms, DPIA for high-risk processing, cross-border transfer procedures, and structured administrative sanctions.
Is PP 33/2026 related to PSE registration with Komdigi?
They are separate but complementary. PSE registration covers electronic systems with Komdigi. PP 33/2026 governs personal data protection within those systems. PSE applications typically require a privacy policy aligned with the PDP Law and PP 33/2026.
How long does it take to prepare a website for PP 33/2026 compliance?
For an MSME online store with one website and a payment gateway, a baseline checklist usually takes two to four weeks: privacy notice, consent forms, data-subject request procedures, vendor audit, and an incident runbook. High-risk features such as AI chatbots or advanced analytics require additional DPIA work.